
You're ready to launch a promotion. Maybe it's a seasonal offer, a service reminder, or a follow-up campaign to leads who already know your business. SMS seems fast. Voice drops seem efficient. Ringless voicemail looks like a way to stay visible without tying up staff time.
Then the doubts start. Can you text that list? Does a prior customer count as permission? Is ringless voicemail treated differently? If someone told your front desk “stop calling me,” would that block future campaigns across every tool your team uses?
That uncertainty is where most small businesses get stuck. Not because they want to ignore the rules, but because do not call list compliance often gets explained in fragments. One article talks about the National Do Not Call Registry. Another talks about TCPA consent. A vendor promises automation but doesn't tell you what internal process still has to exist behind the software.
The practical answer is simpler than the fear around it. Good compliance isn't just a legal shield. It's a discipline of honoring customer choices. Businesses that get this right usually communicate more cleanly, handle complaints faster, and avoid the kind of messy internal confusion that causes preventable mistakes.
Your Guide to Compliant Customer Outreach
A typical small business owner doesn't wake up wanting to become an expert in telemarketing law. They want to fill appointments, confirm orders, revive old leads, and keep current customers engaged. The trouble starts when outreach moves from occasional one-to-one contact to a real system that includes bulk SMS, outbound voice, and ringless voicemail.
That's usually the moment compliance gets treated like a brake pedal. A salon owner hesitates before sending appointment promos. A dental office wants reminders and reactivation campaigns but worries one bad workflow could create legal trouble. An agency managing several local clients realizes each client has a different idea of what “opted in” means.
Why the right frame matters
The businesses that stay out of trouble don't treat compliance as a document sitting in a folder. They treat it like a customer preference system. If someone wants texts but not calls, that matters. If someone revokes permission, that matters more. If your staff can't tell which numbers are suppressed, your legal risk and customer friction rise at the same time.
Practical rule: If your team can't answer “why are we allowed to contact this number?” in plain English, the workflow isn't ready.
What works in real operations
The strongest programs usually share a few traits:
- Clear intake points: Web forms, keywords, checkout flows, and lead forms all say what the person is agreeing to.
- One suppression standard: A person who opts out doesn't get contacted later because one system failed to sync.
- Routine review: Teams don't assume the platform handled everything. They verify.
- Channel-specific judgment: SMS, outbound voice, and ringless voicemail are not interchangeable just because one platform can send all three.
The mistake I see most often is assuming software creates compliance by itself. It doesn't. Software can enforce the rules you define, store consent records, suppress numbers, and reduce human error. But first you need a practical operating model. That starts with understanding the legal layers that apply to outbound outreach.
The Legal Landscape of DNC Compliance
A small business can run one campaign, use one platform, and still answer to three separate do-not-call obligations. Federal rules apply. State rules may add tighter limits. Your own company-specific do-not-call list has to work every time a customer says, "Stop."
That combination is where compliance programs either hold up or break down. A campaign can be acceptable under one rule set and still create exposure under another. The safe approach is operational, not theoretical. Before a call, text, or ringless voicemail goes out, your team needs to know which rules apply, whether the number is suppressed, and where the permission record lives.
Federal rules cover different parts of the problem
The TCPA and TSR are often mentioned together because both affect outbound outreach. They govern different risks.
- TCPA issues usually center on consent, especially for mobile numbers, automated outreach, prerecorded messages, SMS, and ringless voicemail.
- TSR issues usually center on telemarketing practices, including do-not-call obligations and how outreach is conducted.
For a closer look at the consent side, see this guide to TCPA compliance requirements for calls and texts.
In practice, this matters at the campaign setup stage. If a team loads a list into Broadcast and plans to send SMS plus ringless voicemail, the review cannot stop at "we have the numbers." The right question is narrower. What did each contact agree to receive, through which channel, and do you have a record that would hold up if challenged?
State rules change the answer
Federal law is only part of the analysis. States can impose their own do-not-call rules, registration requirements, calling-hour limits, and other restrictions. A national campaign may need different controls depending on where the recipient is located.
Small businesses often get surprised. They approve one script, one list, and one schedule, then assume the same setup works everywhere. It doesn't always. If you are reaching people across state lines, list review and scheduling rules should be checked before launch, not after a complaint.
The risky campaigns are usually the ordinary ones. Old CRM data, broad consent language, and multi-state outreach cause more trouble than obviously abusive calling.
Your internal do-not-call list is the control you own
The national registry gets attention because it is visible. Your internal list is the one your team controls directly, and regulators expect you to honor it.
If a customer tells an agent to stop calling, texts STOP, revokes consent on a web form, or asks to be removed during a voicemail follow-up, that request has to update the system quickly. In Broadcast, that means the number should be suppressed in the relevant workflows so the request is enforced by the platform, not left in a note for someone to remember later.
I tell clients to test this regularly. Submit an opt-out. Check whether the number is blocked from the next SMS send, the next voice campaign, and any saved automation using the same contact list. If one path still allows outreach, the policy is not doing its job.
Understanding the Three DNC Lists
| List Type | Managed By | Applies To | How to Comply |
|---|---|---|---|
| National DNC List | Federal government through the national registry framework | Telemarketing outreach subject to federal do-not-call rules | Scrub campaign lists against the national registry before outreach and make sure exempt assumptions are reviewed carefully |
| State DNC List | Individual states or state regulators where applicable | Outreach into states with their own telemarketing or do-not-call requirements | Check whether each target state has separate rules, registration obligations, or stricter standards before launching campaigns |
| Internal DNC List | Your business | Anyone who told your company they don't want further marketing contact | Record the request promptly, suppress the number across all relevant channels, and keep the suppression in place |
What this means in day-to-day operations
Do not call list compliance is not a single checkbox. It is a repeatable process your staff can follow and your software can enforce.
- Identify which legal rules apply to the campaign
- Check whether the number is on a national, state, or internal suppression list
- Confirm that your consent or exemption record is stored before sending
- Set up your platform so opt-outs update future outreach automatically
That is how legal requirements turn into usable workflow. If your team cannot verify those four points before launch, the campaign is not ready.
Key Exemptions and Common Misconceptions
Most compliance mistakes don't come from open disregard. They come from false confidence. Someone heard that prior customers are exempt, or that B2B is outside the rules, or that ringless voicemail isn't really a call. Those shortcuts are expensive because they feel plausible.
Established business relationship isn't blanket permission
An established business relationship, often called EBR, can affect whether certain outreach is allowed in some contexts. But businesses misuse it when they treat it as permanent, universal permission for any channel, any script, and any campaign.
That's not a safe operating assumption. An existing relationship doesn't erase consent requirements tied to specific technologies or message types. It also doesn't override a direct request to stop.
B2B isn't a free zone
A lot of teams say, “We only call businesses, so we're exempt.” That belief causes sloppy list buying, weak consent capture, and poor suppression practices.
The safer view is this: business outreach can still be regulated, especially when mobile numbers, automated methods, prerecorded messages, or mixed-use numbers are involved. Plenty of sole proprietors and small firms use one number for both business and personal communication. Your CRM may label it “work,” but that label doesn't settle the legal issue.
If your compliance logic depends on everyone else's data being perfectly classified, it isn't reliable enough.
Ringless voicemail still needs caution
Ringless voicemail gets marketed as if it lives in a legal side lane. It doesn't. From a risk-management perspective, you should treat ringless voicemail as a channel that deserves the same careful review you'd give any automated outreach.
That means you shouldn't assume ringless voicemail is exempt from TCPA concerns just because the phone didn't audibly ring. The FCC ruled in 2022 that ringless voicemail is a call under the TCPA and needs consent (FCC 22-85). The operational question is still the same. What permission do you have, how did you get it, and does the recipient have any suppression status that blocks contact?
Narrow exemptions still require discipline
Political organizations, charities, and certain non-sales contacts may fall under different treatment in some contexts. But “exempt” doesn't mean careless. It doesn't mean you can ignore internal requests, skip documentation, or rely on a script someone copied from another organization.
A narrow exemption is exactly that. Narrow.
Misconceptions that cause real problems
- “They gave us their phone number.” A phone number alone is not the same as marketing permission.
- “They bought from us once.” A past purchase doesn't automatically authorize every future channel.
- “They only opted out of texts.” If your consent language and suppression logic aren't clearly separated, channel-specific assumptions can backfire.
- “Ringless voicemail is safer because it feels less intrusive.” Customer perception doesn't decide legal risk.
The better mindset is conservative and operational. If there's ambiguity, tighten the workflow. Make the consent language clearer. Separate channel permissions when appropriate. Suppress broadly when your records are unclear. That approach is less aggressive from a marketing standpoint, but it's much easier to defend and much easier for your team to execute consistently.
Building Your Compliance Operations Playbook
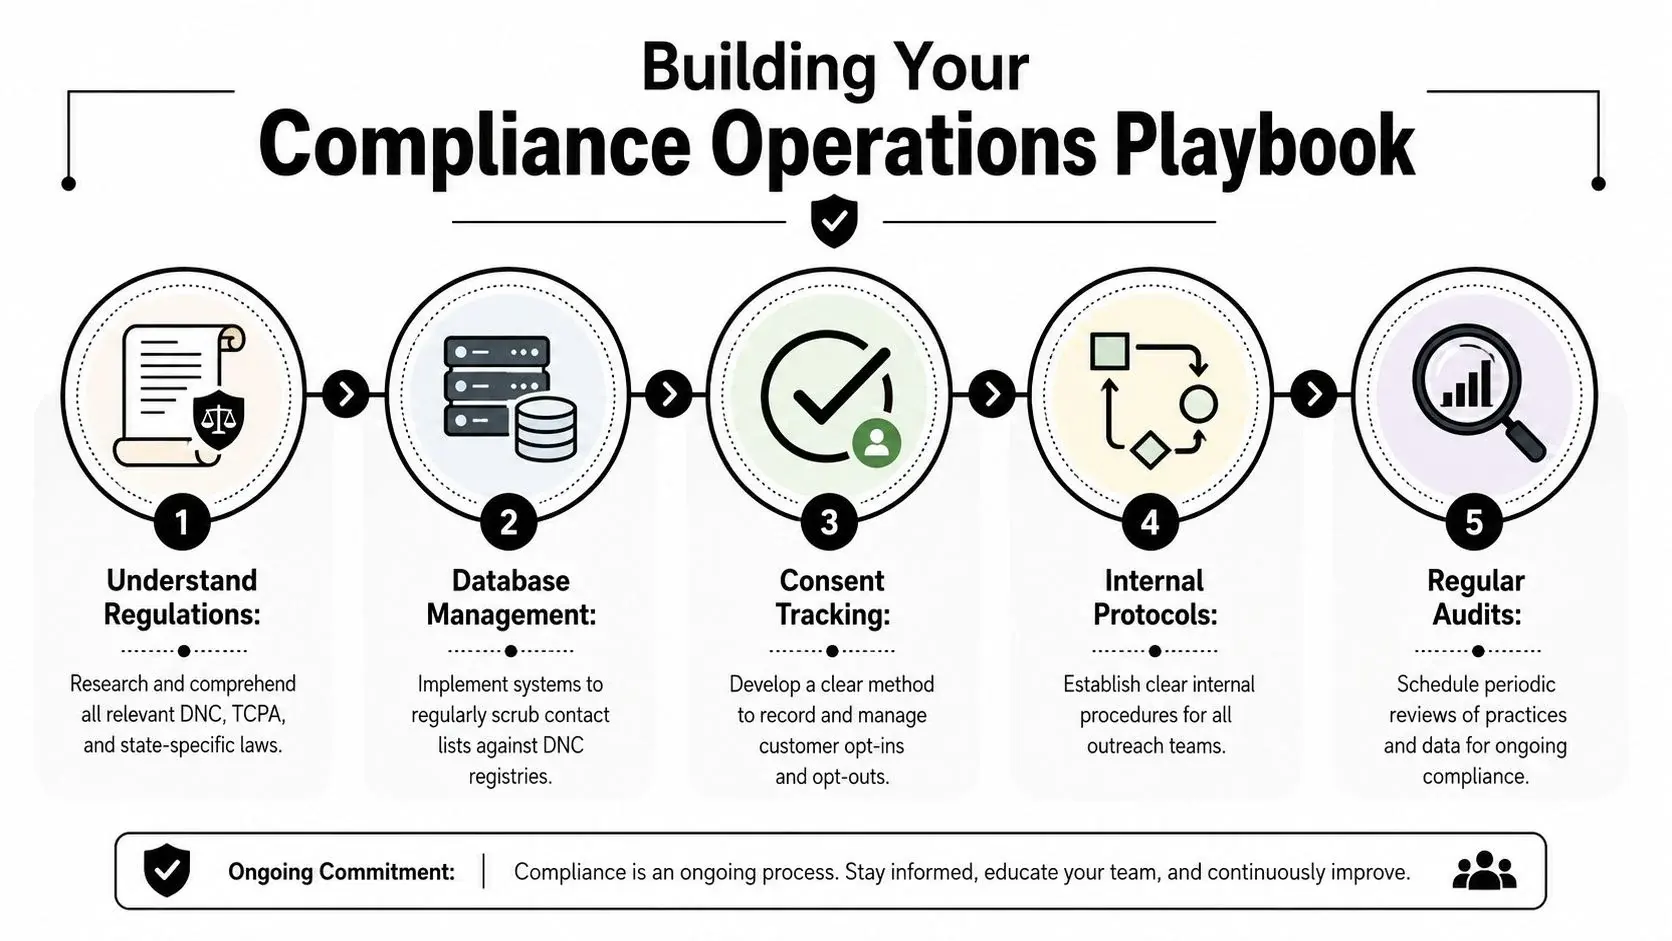
Compliance breaks down when it depends on memory. It holds up when the business uses a repeatable workflow. For most small and mid-sized teams, that workflow needs to cover five areas: rules, data, consent, internal handling, and review.
Start with a written standard
If you don't have a short written policy, your team will improvise. Sales will say one thing, customer support will do another, and whoever uploads the next campaign will guess.
Your policy doesn't need to read like a law review article. It needs to answer practical questions:
- Which channels do we use: SMS, voice, ringless voicemail, or all three.
- What counts as valid permission: Web form opt-in, keyword opt-in, signed intake form, recorded verbal authorization if your counsel allows it, or another approved path.
- Who can approve a campaign: Someone should verify the audience, disclosures, and suppression process before launch.
- How are opt-outs handled: The answer can't be “the team knows.”
For businesses building or staffing this function, it helps to look at how others structure the work. This guide on how to land remote legal compliance work is useful because it shows the kinds of operational skills compliance roles often require, including documentation, process control, and policy handling.
Build list hygiene into the campaign process
Many teams scrub once, then keep reusing the same list in slightly different campaigns. That's where stale data becomes a problem. Every outbound campaign should start with list review, not just message drafting.
A workable process looks like this:
- Validate the numbers so obvious data quality issues are removed early.
- Compare the audience against applicable suppression sources.
- Remove uncertain records when proof is weak or contradictory.
- Tag the approved audience so you know what was reviewed for that specific campaign.
- Store the evidence showing when and how the review happened.
For day-to-day hygiene, a practical resource is this guide to managing contact lists, especially if your database includes leads from forms, imports, events, and manual entry.
Consent capture should be plain and provable
The best consent language is boring. It's specific, readable, and easy to screenshot later if someone questions it. Problems start when businesses hide the disclosure under a button, bundle too many permissions together, or use vague phrases like “stay informed.”
Use forms and intake flows that state what the person is agreeing to receive. If you use SMS keywords, pair them with a clear disclosure path and a confirmation step. If you collect leads from landing pages, store the wording, timestamp, page version, and source details with the contact record whenever possible.
The strongest consent record isn't the longest one. It's the one your team can retrieve quickly and explain without guessing.
Suppression has to be immediate in practice
When someone opts out, speed matters. But consistency matters more. Businesses often process a text opt-out correctly while continuing voice campaigns, or suppress from one brand while another team keeps sending outreach from a related account.
That's why suppression logic should be centralized. The number should move to an internal do-not-contact state that downstream tools, lists, and campaign builders can't casually override.
Keep records that would help in a dispute
You don't need every possible data point. You do need enough evidence to show how contact happened, why it was allowed, and what the business did when preferences changed.
A practical record set usually includes:
- Consent evidence: Form language, source, date, and capture path
- Campaign approvals: Who reviewed the list and when
- Suppression logs: Opt-out request, channel, date, and processing result
- Training records: Which employees were trained on the policy
- Audit notes: Exceptions found and what got fixed
The businesses with the cleanest defense posture aren't the ones with the most software. They're the ones with the clearest chain of events.
Tools and Workflows for Automated Compliance
Manual compliance tends to fail in predictable ways. Someone uploads an old spreadsheet. A customer replies STOP to a text, but the number remains active in a voice campaign. A CRM field says “subscribed,” while a separate messaging tool says “suppressed.” None of those failures look dramatic until a complaint arrives.
Automation helps most when it creates a single source of truth for consent status and suppression status across channels.
Where automation helps most
For SMS, keyword-based opt-in flows are useful because they create a defined entry point instead of relying on a sales rep's memory. Double opt-in tools add another layer of clarity because they help confirm intent and create a cleaner contact trail.
For voice and ringless voicemail, suppression controls matter more than flashy campaign settings. If a platform makes it easy to maintain do-not-call status and apply that status across outbound workflows, you reduce the chance that a customer gets contacted through the wrong channel after opting out elsewhere.
Syncs matter more than features on paper
A lot of businesses have the right tools but the wrong data flow. They collect consent in one system, store customer records in another, and launch outreach from a third. That setup can work, but only if consent and suppression fields stay aligned.
That's where workflow design matters. Teams using CRM integrations or Zapier connections should define exactly which system is authoritative for:
- Opt-in status
- Opt-out status
- Channel permissions
- Timestamp history
- Campaign eligibility
Businesses that want to think more broadly about workflow design can learn a lot from Ekipa AI's automation expertise, especially around reducing manual handoffs and turning repetitive checks into dependable system actions.
Number quality reduces downstream risk
Compliance isn't only about legal permission. It's also about data quality. If a number is invalid, reassigned, miscoded, or entered incorrectly, your campaign logic weakens before the message even goes out.
That's why number validation deserves its own place in the workflow. This resource on validation of numbers is a helpful reminder that cleaner records improve both operational reliability and compliance defensibility.
A compliant campaign starts before the message. It starts when you decide whether that contact record should be in the audience at all.
The strongest setup is boring and centralized
The best automated compliance workflow usually feels uneventful:
- Consent enters through a controlled source
- The record lands in the CRM with relevant flags
- Suppression updates flow back across connected tools
- Campaign builders only see eligible contacts
- Audit logs show what changed and when
That kind of system won't impress anyone in a demo. It will save you from the most common preventable mistakes in SMS, voice broadcasting, and ringless voicemail outreach.
Penalties and Proactive Audits
A business owner usually feels the risk at the worst possible time. A complaint comes in, a vendor asks for proof of consent, or a regulator's letter lands in the inbox. Then the real question shows up. Can you prove why each contact in that campaign was called or texted, and can you show when that person should have been suppressed?
Federal penalties can be severe and they are often assessed per violation. Under the TCPA, a person can sue for $500 per violation, up to $1,500 if the violation is willful (47 U.S.C. 227(b)(3)). The practical problem is volume. A weak process does not create one mistake. It can repeat the same mistake across a full campaign in voice, SMS, and ringless voicemail.
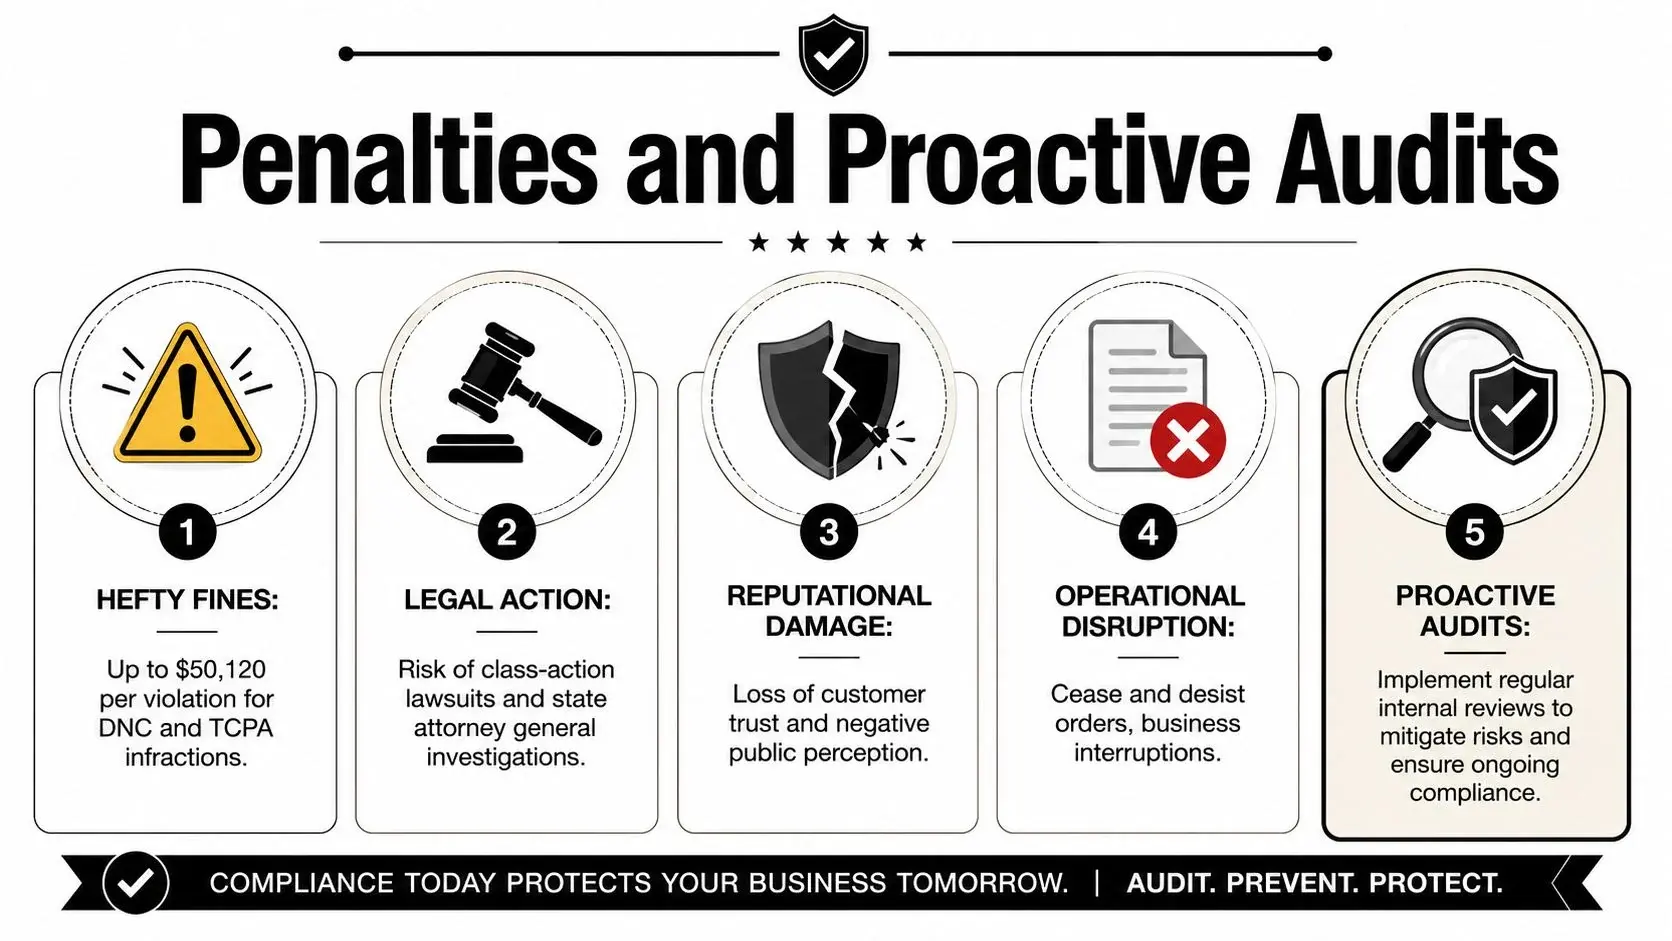
The fix is operational. Audit the system you use, not the policy you hope people follow.
What an owner should audit regularly
Start with one recent campaign inside Broadcast and walk backward. Open the audience, spot-check records, review opt-out status, and confirm the platform history matches your CRM and intake source. If you cannot reconstruct why a contact was included, that is a control failure.
Check these points on a schedule:
- Written policy: Staff need one current policy for internal do-not-call requests, consent handling, and escalation.
- Consent proof: Each marketed contact should have a usable record showing source, date, and channel permissions where applicable.
- Pre-launch review: Someone should approve the audience before launch, and that approval should be documented.
- Suppression sync: An opt-out received in one channel should be reflected anywhere else you market to that person.
- Exception handling: Records with missing source data, conflicting statuses, or manual edits should be routed for review, not sent by default.
If you use Broadcast, this audit should touch actual settings and logs. Review contact fields, list membership, suppression behavior, user permissions, and campaign history. Compliance gets stronger when eligibility is controlled in the tool, not left to memory.
Audit the systems, not just the staff
Training matters, but software failures create repeatable risk faster than a script error. I see this often with imported lists, cloned campaigns, and disconnected opt-out handling between platforms.
Run a few plain checks every month:
- Create seed records with known consent and suppression statuses, then confirm Broadcast treats each one correctly.
- Review a past campaign and verify that suppressed contacts did not slip back in through an import or a copied audience.
- Compare field mapping between your CRM, forms, and Broadcast so opt-in and opt-out values still match.
- Test agency and vendor handoffs if outside partners upload lists, collect leads, or launch campaigns for you.
That discipline applies outside compliance too. Articles like Advisor Momentum's marketing advice make the same point from a different angle. Marketing problems often start with process drift, weak review steps, and assumptions inside the tech stack.
Red flags that deserve immediate attention
Some problems should stop a campaign until they are fixed.
Ask for proof on a random contact record. If your team cannot produce a clear answer quickly, the process is weaker than it looks.
Watch for these warning signs:
- Multiple suppression lists: Sales, support, and marketing should not maintain separate versions of who should not be contacted.
- Legacy or purchased data: Old records with unclear source history create avoidable exposure.
- Channel silos: Voice, SMS, and ringless voicemail rules need to be aligned or opt-outs will be missed.
- No named owner: One person should own pre-launch compliance review, even if several teams contribute data.
- Manual overrides without notes: If users can change statuses in Broadcast or the CRM, those edits need a reason and a timestamp.
A useful audit is small, specific, and repeatable. Pick one campaign, trace ten records, test your suppression controls, and document what failed. Then fix the workflow before the next send.
Sample Policies and Scripts for Your Team
Teams don't follow principles under pressure. They follow scripts, forms, and defaults. If you want do not call list compliance to survive a busy workday, give staff words they can use and a policy short enough to remember.
A simple internal do-not-call policy
Use this as a one-page starting point and tailor it to your business.
Internal Do-Not-Call Policy
- Purpose: Our business respects customer communication preferences and maintains procedures for lawful marketing outreach.
- Scope: This policy applies to all employees, contractors, agencies, and systems that send marketing SMS, voice calls, or ringless voicemail on behalf of the business.
- Consent standard: Marketing outreach may be sent only when the business has an approved basis for contact and supporting documentation where required.
- Do-not-call requests: Any customer request to stop receiving marketing outreach must be recorded promptly and added to the internal suppression process.
- Channel handling: Opt-out requests must be evaluated across all outreach channels, not only the channel where the request was received.
- List use: No campaign may be launched from imported, purchased, or legacy lists unless the list has been reviewed under current compliance procedures.
- Training: Staff who collect phone numbers, manage campaigns, or speak with customers about marketing preferences must follow this policy.
- Escalation: Unclear consent records, disputes, and exception cases must be escalated before any further outreach occurs.
A customer service script for verbal opt-out requests
When a customer says they don't want calls or marketing messages, the staff member should not debate, explain too much, or ask the person to contact another department.
Use language like this:
“I understand. I'll note your request and have your number added to our do-not-contact list for marketing outreach.”
If the customer asks for confirmation:
“We've recorded your request. If you receive anything further, please let us know right away so we can review it.”
That response is calm, direct, and doesn't invite the agent to make legal promises they aren't authorized to make.
A sales script when collecting consent
Sales teams often create risk by speaking loosely. They say “we'll keep in touch” instead of describing what kind of outreach the person is agreeing to receive.
A safer spoken version sounds like this:
- For SMS: “If you'd like, we can send you text updates about offers and reminders. You can opt out at any time.”
- For voice outreach: “We can also contact you by phone about promotions or follow-up related to our services, if you agree.”
- For mixed-channel programs: “If you sign up, we may contact you by text, phone, or ringless voicemail as described in the form.”
Sample web form disclosure language
This should be reviewed for your use case, but the structure matters.
Example disclosure
“By submitting this form, you agree to receive marketing text messages, phone calls, and ringless voicemail messages from [Business Name] at the number provided. Consent is not a condition of purchase. Message frequency may vary. You can opt out according to the instructions provided in the message or by contacting us directly.”
What to train your team to do every time
- Repeat the request clearly: If a customer wants to stop, acknowledge it plainly.
- Log it in the right place: Notes in a private inbox or notebook don't count as a working process.
- Avoid improvising legal answers: Staff should escalate edge cases instead of guessing.
- Use the approved disclosure: Don't let each landing page or intake form invent its own consent language.
Most compliance failures don't start with bad intent. They start with ordinary employees trying to move fast without a usable script. Give them one, and your policies become real.
If your business needs a simpler way to manage outreach across SMS, voice, and ringless voicemail without losing control of consent and suppression workflows, Broadcast is built for exactly that kind of operational discipline. It helps teams organize contact data, automate multi-channel messaging, and keep communication workflows easier to manage as compliance demands grow.


