
You're ready to launch a campaign. The copy is approved, the list is loaded, and the offer is solid. Then someone asks the question that slows everything down: do we have the right consent to send these texts, voicemail drops, and voice broadcasts?
That question matters because TCPA mistakes get expensive fast. Marketing texts sent with an autodialer need prior express written consent, and a person who receives a text that breaks the rules can sue for $500 per violation, which a court can raise to $1,500 if the violation was willful or knowing (47 U.S.C. 227(b)(3)). Each text can count as a separate violation. For any team sending at scale, that's not a minor operational issue. It's legal exposure that can turn a good campaign into a serious problem.
A real sms compliance checklist has to do more than remind you to add “Reply STOP.” It has to connect legal requirements to the way your platform operates: how consent is collected, how opt-outs are enforced, how records are stored, and how message types are separated so a transactional reminder doesn't inadvertently become a promotional violation. That gets even more important when your program includes ringless voicemail, voice broadcasting, appointment reminders, webinar follow-ups, or multi-step drip campaigns.
The practical standard is simple. If you can't prove consent, classify the message correctly, identify the sender, and stop when the recipient says stop, your process isn't finished.
The checklist below is built for operators, not theorists. It focuses on what holds up under audits, what keeps deliverability healthy, and what features in a platform like Broadcast can reduce manual risk before a campaign goes live.
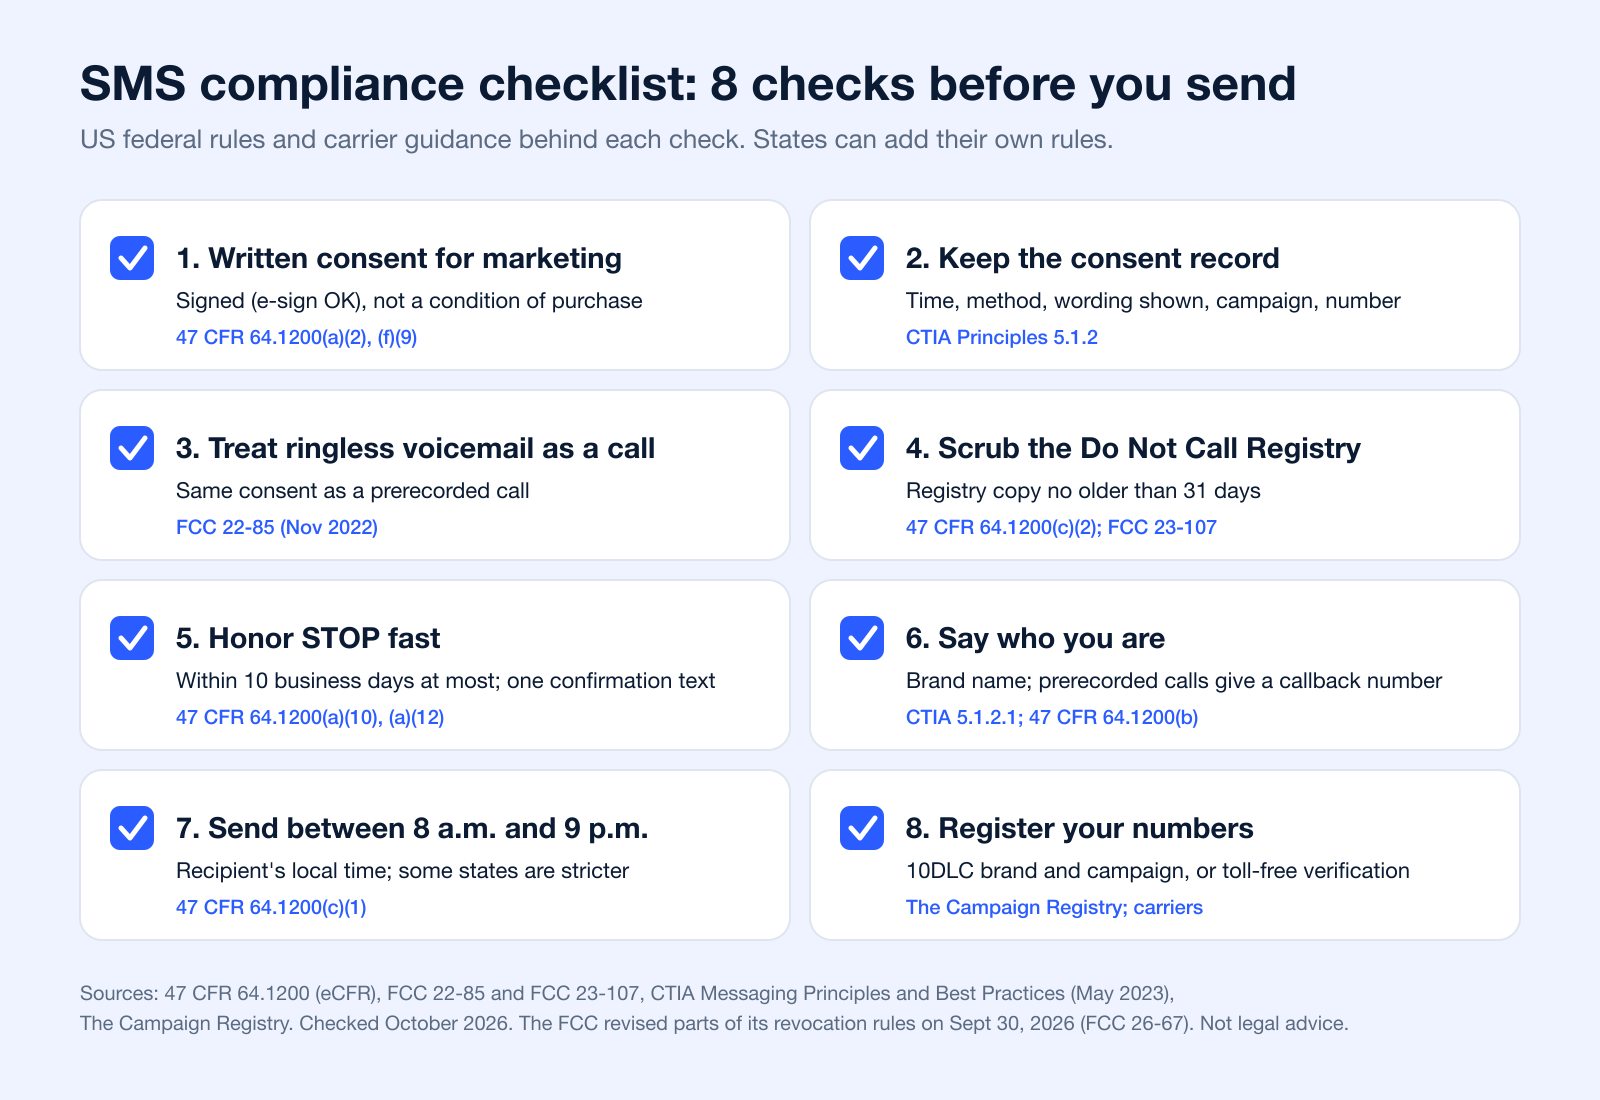
SMS Compliance Checklist at a Glance
Here is the full checklist on one page. Each of the 8 steps below explains how to put it into practice; this summary shows the rule or guideline behind each one, so you can check it against the source.
| Checklist item | What the rule or guideline says | Source |
|---|---|---|
| 1. Consent | Prior express written consent for marketing texts; express consent for informational texts | 47 CFR 64.1200(a)(1), (a)(2), (f)(9); CTIA 5.1 |
| 2. Records | Timestamp, method, wording shown, campaign, IP address, number and identity of the person who consented | CTIA 5.1.2 |
| 3. Ringless voicemail | Counts as a call under the TCPA, so it needs the same consent as a prerecorded call | FCC 22-85 |
| 4. Do Not Call and opt-outs | No marketing texts or calls to registered numbers without permission; registry copy no older than 31 days; STOP honored within 10 business days at most | 47 CFR 64.1200(a)(10), (c)(2), (d); FCC 23-107 |
| Quiet hours | No telephone solicitations before 8 a.m. or after 9 p.m., recipient's local time | 47 CFR 64.1200(c)(1) |
| 5. Sender identity | Program or brand name in the confirmation text; prerecorded messages state the business and a callback number | CTIA 5.1.2.1; 47 CFR 64.1200(b) |
| 6. Health data | Reasonable safeguards; a business associate agreement with a messaging vendor that handles PHI | HHS |
| 7. Monitoring | Watch opt-outs, complaints and delivery by list and campaign | Operational practice |
| 8. Registration and updates | 10DLC brand and campaign registration, or toll-free verification; review rule changes | The Campaign Registry; Twilio |
Two terms come up again and again. Prior express written consent is a written agreement, signed by the person (electronic signatures count), that authorizes marketing messages to a specific number and tells the person that agreeing is not a condition of purchase (47 CFR 64.1200(f)(9)). CTIA is the trade association of the U.S. wireless industry; its Messaging Principles and Best Practices are not law, but carriers and messaging providers apply them, and ignoring them gets messages filtered or blocked.
1. Obtain Prior Express Written Consent Before Sending SMS Messages
A customer fills out a form for a coupon, then gets a promo text, a ringless voicemail, and a follow-up voice broadcast they never expected. That is how consent problems start. The issue usually is not sending volume. It is using broad, vague permission where written consent for marketing was required.
For promotional SMS, businesses need prior express written consent. The same standard should shape how you approach ringless voicemail and voice broadcasts, especially when those channels are part of one campaign flow. Your form, keyword opt-in, or intake process needs to match the outreach you plan to send, and the consent record needs to hold up later. This breakdown of express written consent covers the legal baseline.
A common weak spot is bundling permission into a purchase flow, lead form, or general terms acceptance. That creates risk because the subscriber did not clearly agree to receive marketing texts or prerecorded promotional outreach. Consent also cannot sit in fine print, rely on a pre-checked box, or leave the message type open to interpretation. The FCC rule requires a written agreement that names the number, authorizes marketing messages and says that consent is not a condition of purchase (47 CFR 64.1200(f)(9)).
What compliant opt-in looks like
A defensible opt-in tells the person who is contacting them, what they will receive, and how often. It also separates marketing consent from other permissions, such as account updates, appointment reminders, or customer service messages. If you plan to use more than one channel, say so. SMS consent language should not subtly expand into ringless voicemail or voice broadcasting later.
That is where platform setup matters. In Broadcast, the safest approach is to build separate entry points and lists by communication type, then map automations to the consent collected for each one. A checkout form for promotional texts should feed an SMS marketing list. A reminder intake form should feed a transactional list. A ringless voicemail campaign should only pull from contacts who agreed to that kind of outreach. Good compliance operations are built in the workflow, not patched on after launch.
Use opt-in language that includes:
- the business name or brand sending the messages
- the specific message type, such as promotions, reminders, or follow-ups
- expected message frequency
- a statement that consent is not a condition of purchase
- notice that message and data rates may apply
- links to Terms & Conditions and Privacy Policy presented clearly and separately
The examples matter. An ecommerce brand can collect SMS promo consent at checkout with an unchecked box that names the brand and states the customer is agreeing to receive recurring marketing texts. A healthcare clinic can collect written permission for appointment reminders in a dedicated intake workflow, while keeping promotional offers separate. A local service business running SMS and ringless voicemail should use distinct checkboxes or disclosures for each channel so the contact record reflects what the person approved.
Practical rule: If the subscriber could reasonably say, “I agreed to updates, not marketing,” your opt-in language needs work.
Which Consent Each Type of Text Needs
CTIA sorts business texts into three groups by what the message does, and the FCC rule draws the same line between marketing and everything else.
| Type of text | Examples | Consent expected | Source |
|---|---|---|---|
| Conversational | The customer texts first and you reply to the question | Implied: the customer started the exchange | CTIA 5.1 |
| Informational | Appointment reminders, welcome texts, order and delivery alerts | Express consent; for automated texts to cell phones, prior express consent | CTIA 5.1; 47 CFR 64.1200(a)(1) |
| Promotional (marketing) | Sales, coupons, product launches, anything that asks people to buy | Prior express written consent | CTIA 5.1; 47 CFR 64.1200(a)(2) |
CTIA also notes that adding a call to action, such as a coupon code, to an informational text "may place the message in the promotional category." For sample consent wording and confirmation texts, see this guide to the opt-in text.
Double opt-in is often worth the extra step, even though it is not required: CTIA's Short Code Monitoring Handbook says recurring programs must send one message confirming opt-in and that "double opt-in is optional." It creates a cleaner record, catches bad numbers early, and gives you one more checkpoint before a contact enters an automated sequence. That helps more when campaigns branch across SMS, voicemail drops, and voice broadcasts, because one bad assumption at signup can spread across every channel you use.
2. Maintain Detailed Records of All Consent and Opt-Out Requests
A complaint comes in six months after launch. The contact says they never agreed to marketing texts, your team has changed vendors twice, and no one can pull the original signup language. That is how a routine campaign turns into a compliance problem.
Recordkeeping is the proof layer for SMS, ringless voicemail, and voice broadcasts. You need a clear history of what the person agreed to, which channel that consent covered, when they opted out, and whether your platform stopped future sends fast enough. If that record is scattered across forms, inboxes, and spreadsheets, enforcement breaks down.
What your records need to show
Store enough detail to answer four questions without guesswork: who consented, how consent was captured, what disclosures were shown, and what happened after any opt-out request.
CTIA lists the data it expects senders to keep for each opt-in, "where applicable": the timestamp, the consent medium (web form, paper form, SMS keyword), the language and action used to get consent, the specific campaign, the IP address, the phone number, and the identity of the person who consented (CTIA 5.1.2).
For each contact, keep:
- Consent timestamp and source: Date, time, form, landing page, keyword, import source, or agent workflow that captured permission.
- Channel-specific permission: Separate records for SMS, ringless voicemail, and voice broadcasting so one approval is not applied to every channel.
- Disclosure version: The exact consent language, terms link, privacy link, and message type shown at the moment of signup.
- Contact data used: The phone number submitted, any associated account or location, and the user or system that created the record.
- Opt-out events: STOP, END, CANCEL, HELP-driven support handling, agent-entered revocations, and manual suppression updates with timestamps.
- Delivery and campaign history: Which campaigns were sent, from which number, and whether suppression rules blocked later outreach.
That level of detail matters in real disputes. If a recipient opted into appointment reminders but never approved promotions, your logs need to show that difference. If they revoked consent by replying STOP after an SMS, your system should suppress later text campaigns and flag the number for related voice workflows based on your policy.
Keep the audit trail usable
Saving logs is not enough. Teams need to retrieve them quickly by phone number, campaign, list, keyword, or account owner.
That is where platform design matters. In a tool like Broadcast, the practical goal is simple: every opt-in, send, reply, voicemail drop, and suppression event should be attached to the contact record automatically. The best setups also preserve form language versions, record reply keywords in real time, and prevent staff from re-adding opted-out numbers without an admin review step.
Treat suppression data as operational data, not archive data. If someone opts out in one workflow and another campaign can still reach them because lists do not sync, the problem is not legal theory. It is system configuration.
Build a recordkeeping process your team will actually follow
Use automated logging for the events that create the most risk:
- Web form opt-ins: Capture the submission time, page URL, disclosure copy, and submitted number.
- Keyword opt-ins: Store the keyword, short code or long code used, and the confirmation response.
- Agent-assisted enrollments: Record the employee, call outcome, script version, and the written consent source tied to the enrollment.
- Opt-out requests from any channel: Log SMS replies, voicemail callback requests, live agent removals, and support tickets in one suppression history.
- List imports and CRM syncs: Keep an import log that shows where the data came from and whether consent status was verified before activation.
Good records do two jobs. They support your position if a complaint reaches counsel or a carrier. They also expose weak spots early, such as a form collecting SMS consent without matching suppression rules for ringless voicemail or broadcast calls.
If you cannot produce the consent record and opt-out history in a few minutes, the process needs work.
How Long to Keep Consent and Opt-Out Records
No federal rule sets one retention period for SMS consent records, but two dates are useful. A company-specific do-not-call request must be honored for 5 years from the time it is made (47 CFR 64.1200(d)(6)), so that suppression entry has to outlive it. And the general federal deadline to file a lawsuit under a federal law passed after 1990, which includes the TCPA, is 4 years after the claim arises (28 U.S.C. 1658(a)). Many teams keep consent records at least that long; ask counsel what fits your program. CTIA also asks senders to process phone number deactivation files regularly (for example daily) and remove disconnected numbers from opt-in lists (CTIA 5.1.5).
3. Implement Ringless Voicemail Compliance and Disclosure Requirements
Ringless voicemail looks simple from the outside. Record a message, drop it into voicemail, track responses. In practice, it creates the same compliance pressure points as SMS and voice broadcasting, plus a few of its own.
The baseline rule is straightforward. Don't treat ringless voicemail as a loophole. In November 2022 the FCC ruled that ringless voicemail is a "call" under the TCPA (FCC 22-85), so a prerecorded voicemail drop to a cell phone needs the same consent as a prerecorded call: prior express consent, and prior express written consent when it is marketing. The safe operating posture is the one disciplined teams use for SMS marketing: explicit consent, accurate records, clear identification, and immediate respect for opt-out requests. This guide to ringless voicemail compliance covers the details.
What to say in the message
A compliant ringless voicemail should identify the business, provide a valid callback number, and make it obvious that the recipient is hearing a voicemail from your company. That matters because vague intros and anonymous caller identity create complaints fast. The message should also avoid drifting into misleading urgency or hidden sales language.
The FCC rule spells this out for every artificial or prerecorded voice message: state the identity of the business at the beginning, and state a callback number during or after the message (47 CFR 64.1200(b)(1)-(2)). Marketing messages must also offer an automated opt-out, and when the message is left on voicemail, a toll-free number that reaches that opt-out (47 CFR 64.1200(b)(3)). Since February 2024, AI-generated voices count as "artificial" voices under the same rules (FCC 24-17).
A few common examples:
- Event organizers: Send a voicemail reminder to registered webinar attendees who already opted in to event communications.
- Service businesses: Notify customers about schedule changes or confirmed appointments without forcing a live pickup.
- Sales teams: Follow up after a missed call only when the contact has given permission for that type of outreach.
- Karate studios and schools: Share weather closures or class updates with families who enrolled for mobile notifications.
The trade-off is reach versus scrutiny. Ringless voicemail can feel less intrusive than a live call, but the moment a voicemail includes a sales pitch the consent standard gets tighter and the classification matters more. That's where teams get in trouble. They start with operational reminders, then tack on an offer at the end.
A practical setup in Broadcast is to separate ringless voicemail campaigns by purpose, keep recordings specific to that purpose, use custom caller ID that matches the business, and log each successful drop for tracking and billing. Since Broadcast supports ringless voicemail delivery to mobile and landline inboxes, along with scheduling and unlimited recordings, the operational side is there. Your compliance process still has to define who can receive what and why.
If a voicemail starts as a reminder and ends as a promotion, regulators and carriers may treat it like a promotion.
4. Comply with National DNC Registry Requirements and Provide Clear Opt-Out Mechanisms
A familiar failure looks like this. A customer texts STOP after a promotion, gets removed from SMS, then still receives a ringless voicemail offer two days later because the voice list came from an older export. That single gap can trigger complaints fast.
DNC compliance has to work across channels, not inside separate tools. For SMS, voice broadcasting, and ringless voicemail, use two suppression controls every time. Keep an internal do-not-contact list and scrub outbound lists against the National Do Not Call Registry and any other applicable lists before launch. Then make sure opt-outs update the contact record that every campaign uses. More detail is in this guide to Do Not Call list compliance.
Speed matters here. If someone revokes permission, the safe move is to stop promotional outreach immediately in practice, even if a vendor workflow allows a processing window. Waiting for manual cleanup creates avoidable risk, especially when sales, marketing, and operations each run their own campaigns.
| Rule | What it requires | Source |
|---|---|---|
| National DNC Registry | No telephone solicitations to registered residential numbers; the FCC confirmed in December 2023 that this covers marketing texts to wireless numbers | 47 CFR 64.1200(c)(2); FCC 23-107 |
| Registry scrubbing | Safe harbor requires a registry copy obtained no more than 31 days before the call, plus records of the process | 47 CFR 64.1200(c)(2)(i)(D) |
| Internal do-not-call list | Written policy, trained staff, record requests when made, honor them within 10 business days, keep them 5 years | 47 CFR 64.1200(d) |
| Text opt-outs | Replies such as stop, quit, end, revoke, opt out, cancel or unsubscribe revoke consent; honor within 10 business days at most | 47 CFR 64.1200(a)(10) |
| Opt-out confirmation | One confirmation text with no marketing; presumed fine if sent within 5 minutes | 47 CFR 64.1200(a)(12); CTIA 5.1.3 |
The FCC revised parts of these revocation rules on September 30, 2026 (FCC 26-67), including letting people stop specific categories of messages, so check the current text before you launch.
Build one suppression system for every outreach channel
The strongest setup is one contact record, one permission model, and one suppression rule set applied to SMS, ringless voicemail, and voice broadcasts.
Use controls like these:
- Automatic keyword handling: Recognize the opt-out words the FCC lists (STOP, QUIT, END, REVOKE, OPT OUT, CANCEL, UNSUBSCRIBE) plus normal-language requests, update the record without staff intervention, and answer HELP with support information. This guide to the unsubscribe text message covers the reply.
- Cross-channel suppression sync: If a contact opts out of promotional texts, review whether that opt-out should also block promotional ringless voicemail and voice campaigns based on your consent language and campaign purpose.
- Registry scrubbing logs: Save the scrub date, list source, match results, and the user or system that approved the send.
- Shared campaign governance: Use the same suppression logic for mixed sequences so a contact is not active in SMS but suppressed in voice, or the reverse.
Platform controls save teams from their own process gaps. In a tool like Broadcast, the practical benefit is not just sending messages. It is centralizing contact data, automating opt-out handling, and applying suppression rules before an SMS blast, voicemail drop, or voice broadcast goes out. The software can enforce the rule, but your team still has to define the rule correctly.
One more trade-off matters. Aggressive list growth can increase reach, but older imported data usually creates more DNC matches, more opt-outs, and more complaints. Clean lists often outperform larger lists because they reduce waste and keep your sending program stable.
Respect Quiet Hours
The federal rule bans telephone solicitations to residential subscribers before 8 a.m. or after 9 p.m., local time at the recipient's location (47 CFR 64.1200(c)(1)). Some states set shorter windows for marketing calls, so check whether yours applies to texts. Schedule by the contact's time zone, not your own.
5. Clearly Disclose Sender Identity and Include Valid Callback or Contact Information
Anonymous outreach gets filtered, ignored, or reported. In compliant messaging, every text, voice broadcast, and ringless voicemail should tell the recipient who is contacting them and how to respond.
For SMS, that means including your business or program name and a clear opt-out instruction; CTIA lists the program name, customer care contact, opt-out, frequency and fees as the items of the first confirmation text (CTIA 5.1.2.1). Links and phone numbers inside a message should not hide who is sending it (CTIA 5.3.2 and 5.3.3). Carriers also restrict SHAFT content (sex, hate, alcohol, firearms, tobacco): CTIA's Short Code Monitoring Handbook lists it, with gambling and sweepstakes, as content that is "either explicitly prohibited or has additional Wireless Provider requirements," such as an age gate. Register your sender: 10DLC brands and campaigns are verified by The Campaign Registry before they send, and toll-free numbers need verification.
Recognition beats cleverness
Teams sometimes try to save characters in SMS by removing the company name or replacing it with a vague abbreviation. That usually backfires. If the recipient doesn't immediately recognize the sender, trust drops and complaints go up.
A few practical examples:
- An ecommerce store should open with its brand name and use a monitored support number.
- A dental office should identify the clinic by name in appointment reminders.
- A webinar host should name the event or organization so the message doesn't look like a random blast.
- A sales rep using voice broadcasting should make sure the caller ID and callback number map to the actual business.
For live and prerecorded telemarketing calls, the rule is explicit: give the name of the caller, the business on whose behalf the call is made, and a telephone number or address where it can be reached (47 CFR 64.1200(d)(4)).
This is one place where consistency matters more than creativity. Use the same sender identity across campaign types when possible. If your SMS comes from one name, your ringless voicemail from another, and your voice broadcast caller ID from a third, recipients treat that as suspicious even before they hear the offer.
“Recognizable beats optimized.” A slightly longer message from a known sender usually outperforms a shorter message from an unknown one.
6. Ensure HIPAA Compliance for Healthcare Communications and Patient Data
Healthcare teams have an extra layer of risk. It's not just about consent and opt-outs. It's also about what patient information appears in the message, where that information is stored, and whether your vendor can support healthcare obligations.
Broadcast positions healthcare messaging around secure workflows and supports HIPAA-ready communications, including features relevant to patient outreach in its overview of HIPAA-compliant patient communication. That matters when you're sending appointment reminders, refill notifications, post-discharge follow-ups, or ringless voicemail reminders to verified patient numbers.
Keep patient messages minimal
The safest healthcare messages are usually the least detailed ones. A dental office can send an appointment reminder with the practice name, date, and callback number. A therapy clinic can confirm the time of a session without including sensitive treatment details. A medical equipment provider can remind a patient about service timing without listing protected clinical context.
Healthcare teams should also pay attention to the vendor relationship. HHS lists a vendor that provides "patient messaging" on behalf of a covered entity as an example of a business associate, and a covered entity may share protected health information with it only with a business associate agreement (BAA) in place (HHS business associate guidance). HHS also says providers may communicate electronically with patients "provided they apply reasonable safeguards," such as "limiting the amount or type of information disclosed" (HHS FAQ 570).
Use this operating standard:
- Limit PHI: Include only what the patient needs to act.
- Verify numbers: Confirm the mobile number belongs to the patient or authorized contact before campaign enrollment.
- Control access: Restrict who can build lists, write templates, and view logs.
- Execute BAAs where needed: Don't assume a messaging vendor is suitable for healthcare use without the right contractual and technical posture.
One TCPA detail matters here too: the FCC rule exempts from the written-consent requirement a call or text that delivers a "health care" message by or on behalf of a HIPAA covered entity or its business associate (47 CFR 64.1200(a)(2)). That exemption does not cover promotions, so keep marketing offers on a separate, written-consent list.
In multi-location practices, the practical win comes from standard templates. If each office writes its own reminders, someone eventually includes more patient information than they should. Centralized templates and approval controls reduce that risk.
7. Monitor Campaign Performance Metrics and Complaint Rates to Identify Compliance Issues
A compliance problem often shows up in campaign metrics before it shows up in a complaint email. That's why list quality, opt-out behavior, and deliverability aren't just marketing concerns. They're compliance signals.
Benchmarks help you spot outliers. MessageFlow's 2026 SMS marketing benchmarks put SMS unsubscribe rates below 3.5% per send, with well-managed programs at 0% to 1.5%, and an average click-through rate of roughly 19%. Treat figures like these as one vendor's warning thresholds, not legal standards: a sudden jump in opt-outs on your own list matters more than any industry average.
Use metrics as compliance diagnostics
If unsubscribe rates jump, don't just tweak copy. Check whether the audience expected that message type. If delivery slips, verify registration, sender setup, and list source. If clicks collapse but opens stay high, your offer may be weak. If both opt-outs and complaints rise together, your consent quality may be the problem.
Broadcast's analytics, click tracking, number validation, and segmentation tools are useful here because they let operators trace issues to a list, segment, message, or workflow rather than guessing (see deliverability). For voice broadcasting and ringless voicemail, monitor response patterns and suppression activity the same way. A bad voicemail script can trigger the same trust breakdown as a bad text campaign.
Watch for these patterns:
- Higher opt-outs after list imports: Often a sign the original consent language was weak or disconnected from the current campaign.
- Lower delivery in one campaign type: Usually points to registration, filtering, or stale numbers.
- Complaint concentration by segment: Suggests a targeting or classification issue, not a universal messaging problem.
- Mismatch across channels: If SMS performs cleanly but ringless voicemail draws pushback, the problem may be message framing rather than audience quality.
Don't wait for legal trouble to start auditing. The dashboard usually tells you first.
8. Stay Updated on Evolving State and Federal SMS and Voice Regulations
Compliance rules don't stand still. Carrier standards shift, CTIA guidance changes, 10DLC enforcement evolves, and state-level rules can create extra requirements for the same campaign.
That's especially important in mixed-channel programs. A team might have clean SMS consent language, but weak ringless voicemail disclosures. Or they may treat transactional and promotional traffic as interchangeable across automation steps, which is where many avoidable violations start.
Classification errors create most of the mess
One of the most overlooked issues in a modern SMS compliance checklist is the line between transactional and promotional messaging. Many checklists focus on strict marketing consent and say less about keeping informational messages (express consent) apart from promotional ones (prior express written consent) in multi-channel workflows. CTIA is clear that adding a call to action, such as a coupon code, to an informational text "may place the message in the promotional category" (CTIA 5.1).
That problem gets worse when automations combine SMS, voice broadcasting, and ringless voicemail in one sequence. A shipping update is transactional. Add a discount teaser, and you've changed the legal profile of the message.
A platform can help if it enforces structure. Broadcast's campaign controls, drip sequencing, segmentation, and registration support are useful when they're paired with policy. Accordingly, Broadcast's 10DLC compliance guidance becomes operationally important. Register the brand and use case correctly, separate campaign types, and don't let convenience blur consent categories.
Regulatory updates rarely break compliant systems overnight. They expose weak workflows that were already too loose.
What Changed in SMS and Voice Compliance (2022 to 2026)
- November 2022: the FCC ruled that ringless voicemail is a call under the TCPA (FCC 22-85).
- September 1, 2023: Twilio began blocking all unregistered 10DLC traffic to U.S. numbers (Twilio changelog).
- December 2023: the FCC codified Do Not Call Registry protections for marketing texts (FCC 23-107).
- January 31, 2024: Twilio began blocking traffic from toll-free numbers that are not verified (Twilio error 30032).
- February 2024: AI-generated voices count as artificial voices under the TCPA (FCC 24-17).
- February 1, 2025: Bandwidth says unregistered 10DLC traffic "is being blocked in the industry" (Bandwidth 10DLC FAQ).
- September 30, 2026: the FCC adopted new consent revocation rules (FCC 26-67). Check the effective date and current text before relying on any revocation detail above.
Set a recurring review cadence with legal or compliance owners, especially if you operate across states, run healthcare communications, or manage agency accounts. The teams that stay clean aren't the ones with the longest policy manuals. They're the ones that update workflows before bad habits harden.
8-Point SMS Compliance Comparison
| Item | Implementation complexity | Resource requirements | Expected outcomes | Ideal use cases | Key advantages |
|---|---|---|---|---|---|
| Obtain Prior Express Written Consent Before Sending SMS Messages | Medium–High: process design and verification (double opt-in) | Consent capture tools (forms/keywords), audit trails, staff training | Lower TCPA risk; higher deliverability and defensibility | Promotional SMS, appointment reminders, events | Defensible documentation; increased trust and deliverability |
| Maintain Detailed Records of All Consent and Opt-Out Requests | High: robust logging, retention and export capabilities | Secure storage, automated logging, encryption, compliance reports | Audit-ready records; faster dispute resolution | Regulated sectors and large-scale campaigns | Legal defensibility; quick opt-out enforcement |
| Implement Ringless Voicemail Compliance and Disclosure Requirements | Medium–High: technical delivery + evolving legal requirements | Ringless platform, consent records, callback numbers, delivery tracking | Improved reach and engagement but higher regulatory scrutiny | Reminders, webinar follow-ups, scalable outreach | Cost-effective reach; trackable delivery metrics |
| Comply with National DNC Registry Requirements and Provide Clear Opt-Out Mechanisms | Medium: integration and routine scrubbing | DNC access/integration, automated scrubbing, opt-out processing systems | Reduced TCPA/DNC violations; cleaner contact lists | Large marketing and voice campaigns, multi-state outreach | Lowers DNC risk; preserves brand reputation |
| Clearly Disclose Sender Identity and Include Valid Callback/Contact Information | Low–Medium: template and caller ID configuration | Branded numbers/short codes, caller ID auth, message templates | Fewer complaints; higher engagement and response rates | All outbound messaging (SMS, voice, voicemail) | Builds trust; reduces spam reports and abuse |
| Ensure HIPAA Compliance for Healthcare Communications and Patient Data | High: strict security and BAA management | Reasonable safeguards (such as encryption), secure storage, BAAs, staff training | Protected PHI; compliance with HIPAA; reduced penalties | Healthcare providers, clinical messaging, patient notifications | Strong privacy protections; legal and regulatory compliance |
| Monitor Campaign Performance Metrics and Complaint Rates to Identify Compliance Issues | Medium: dashboards, alerts and review processes | Analytics platform, alerting, staff/analyst time | Early detection of compliance risks; improved campaign performance | Ongoing campaigns, marketing agencies, operations | Proactive risk management; data-driven remediation |
| Stay Updated on Evolving State and Federal SMS/Voice Regulations and Regulatory Guidance | Medium: continuous monitoring and policy updates | Legal counsel/subscriptions, compliance team time, training | Timely adaptation to new rules; reduced surprise liability | Multi-state operations and regulated industries | Proactive compliance; avoids unintended violations |
SMS Compliance Checklist FAQ
What Should Be on an SMS Compliance Checklist?
At minimum: the right consent for each message type, a stored consent record, opt-out handling that honors STOP within 10 business days at most, Do Not Call scrubbing, quiet hours, clear sender identity, 10DLC or toll-free registration, and safeguards for any health data. The table at the top of this guide lists the source for each item.
Do Transactional Texts Need Consent?
Yes, but a lighter kind. Informational texts such as reminders and order alerts need express consent, which can be oral; automated marketing texts need prior express written consent (CTIA 5.1; 47 CFR 64.1200(a)(1)-(2)). Adding an offer to a reminder can turn it into a marketing text.
Does the Do Not Call Registry Apply to Text Messages?
Yes for marketing texts. In December 2023 the FCC codified that texters need the consumer's prior express invitation or permission before sending a marketing text to a wireless number on the National Do Not Call Registry (FCC 23-107).
What Are the Penalties for Breaking SMS Rules?
Under the TCPA, a recipient can sue for actual losses or $500 per violation, whichever is greater, and a court can triple that to $1,500 if the violation was willful or knowing (47 U.S.C. 227(b)(3)). Carriers can also filter or block traffic that breaks their guidelines.
Is Double Opt-In Required for SMS?
No. CTIA says recurring programs must send one opt-in confirmation and that "double opt-in is optional" (Short Code Monitoring Handbook). It is still a good way to confirm that the phone's owner signed up.
What Hours Can You Send Marketing Texts?
Federally, between 8 a.m. and 9 p.m. in the recipient's local time (47 CFR 64.1200(c)(1)). Some states are stricter, so check the rules where your contacts live.
Do I Need 10DLC Registration?
If you send business texts from a standard 10-digit number to U.S. phones, yes. Unregistered 10DLC traffic is blocked (Bandwidth). This guide to 10DLC compliance walks through it.
Turn Compliance into a Competitive Advantage
Many teams approach compliance like a braking system. They assume it slows campaigns down, limits creativity, and creates extra admin work. In practice, the opposite is usually true. A clean messaging program reaches better contacts, gets fewer complaints, and gives your team more confidence to scale SMS, voice broadcasting, and ringless voicemail without crossing lines they can't defend later.
That's why a real sms compliance checklist needs to be operational, not theoretical. Consent collection has to be tied to specific forms, keywords, and disclosures. Opt-outs have to suppress every relevant channel, not just one list in one tool. Message classification has to stay clean so reminders don't inadvertently become promotions. Recordkeeping has to be strong enough that if someone challenges a campaign months later, your team can pull the logs and show exactly what happened.
The businesses that do this well usually share the same habits. They separate transactional and promotional workflows. They keep sender identity consistent. They use double opt-in when list quality matters. They centralize suppression logic. They treat ringless voicemail with the same seriousness they give SMS marketing, instead of treating it like a workaround. And they review metrics for warning signs before a complaint turns into a legal problem.
Broadcast is useful here because it connects compliance work to execution. Double opt-in, DNC management, number validation, segmentation, click tracking, scheduling, voice and ringless voicemail controls, and HIPAA-ready support give teams the pieces they need to build compliant outreach into the workflow itself. That matters more than having a policy document nobody checks. If the platform can automate safer defaults, your team makes fewer mistakes under pressure.
There's also a brand upside. Recipients respond better when they know who's contacting them, why they're being contacted, and how to stop it if they want. Carriers also reward that discipline through stronger deliverability and less filtering pressure. Compliance, in other words, isn't separate from performance. It supports it.
The practical goal isn't perfection. It's defensible consistency. Build a system where consent is captured clearly, disclosures are visible, sender identity is obvious, healthcare data is protected when relevant, and every stop request is honored fast across SMS, voice, and ringless voicemail. That's how you reduce exposure and keep outreach productive over the long term.
If you want a platform that makes compliant outreach easier to run day to day, Broadcast gives you the tools to manage SMS, voice broadcasting, and ringless voicemail from one place. You can automate double opt-in, manage DNC suppression, segment audiences, schedule campaigns, track clicks and responses, and support HIPAA-ready communications without piecing together separate systems. For teams that need scalable outreach with fewer compliance gaps, Broadcast is a practical place to start.


